External DPO and nFADP consulting
The fully revised Federal Act on Data Protection (nFADP) has been in force since 1 September 2023. For many companies it meant new obligations to put into practice; for those handling customer data in the European Union, the GDPR applies on top of the Swiss law.
From Lugano we work for companies in Ticino and the rest of Switzerland as an external DPO, or alongside the person you've already appointed.
What we handle
External DPO
We take on the role or support your internal one, and act as the point of contact with the authorities.
Compliance check
We look at how you process data today, where the gaps are and what needs fixing first.
Records of processing activities
We set them up and keep them up to date.
Impact assessments
We prepare them for the processing that requires them.
Training
Half-day sessions with the people in your company who handle data every day.
Data subject requests
Customers or employees asking what data you hold about them: the answer must be given within 30 days, and we prepare it.
Contracts with processors
Anyone processing data on your behalf, from your business software to your newsletter tool, needs a written agreement: we check and complete them.
Breaches
We help you respond and notify the FDPIC and the people affected.
Privacy on your website and tools
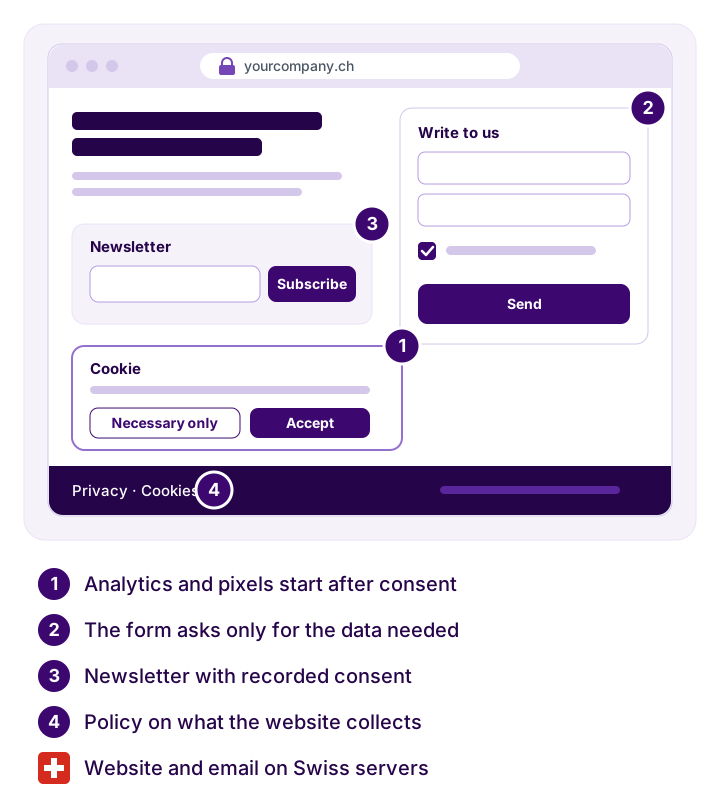
Much of a company's data now passes through digital channels: the contact form, the newsletter, Google Analytics, campaigns, cloud software. Since we also build websites and handle hosting and marketing, we sort out data protection at the points where the data actually flows:
Privacy policy
Written based on what the website actually collects.
Cookie banner
Analytics and advertising pixels that only start after consent.
Forms and newsletters
Only the data that's needed, with consent recorded.
Where the data lives
Hosting and email in Switzerland, and a check of the services that send it abroad.
Artificial intelligence
We're preparing a guide on how to use ChatGPT and other AI tools in your business, and on what not to paste into them: customer data, contracts, confidential information.
For the websites we build ourselves, this work starts at the planning stage: see website design and hosting and IT support.
What the nFADP requires
Since the revision came into force on 1 September 2023, companies must, depending on the case:
- inform people when they collect their data, for example with the privacy policy on the website
- keep records of processing activities, which companies with fewer than 250 employees and low-risk processing are exempt from
- carry out an impact assessment for high-risk processing
- report to the FDPIC any data security breaches that pose a high risk
- process data only for lawful, recognisable and proportionate purposes
The most serious intentional violations are punishable by a fine of up to CHF 250,000, imposed on the person responsible.
How we work
Initial snapshot
What data you process, where it's stored and who has access.
Compliance plan
Tasks, priorities and roles, in order of urgency.
Putting it into practice
Documents, records and procedures, written and adopted.
Over time
Regulatory updates, training and support when needed.
Who it's for
For companies that process data about customers, patients or employees and have nobody in-house to keep on top of it.
- companies processing sensitive personal data
- anyone who sells or markets to the European Union and falls under the GDPR
- anyone who has appointed an internal data protection officer and wants to back them with outside expertise
- anyone with a website that has a contact form, newsletter or analytics and has never checked the privacy policy
Costs
The external DPO role is provided for an ongoing fee. Compliance checks and impact assessments are quoted per job, and many companies start there.
Frequently asked questions
Can you take on the role of external DPO?
Yes, or we can support someone already appointed in your company.
Does the service cover both the GDPR and the nFADP?
Yes, we work with both: the Swiss law and, where it applies, the European regulation.
Is appointing a DPO mandatory?
Not for every company. In Switzerland, appointing a data protection advisor is optional for private companies, while the GDPR requires it in certain cases. It's still advisable for anyone processing sensitive data or data on a large scale.
Do you also offer one-off work?
Yes. You can just have the compliance check, or carry on with ongoing support.
Does my website comply with the nFADP?
You can tell by looking at what it collects: forms, cookies, analytics, advertising pixels, newsletters. We compare the privacy policy and cookie banner with what the website actually does, and fix them if needed.
What happens if there's a data breach?
We help you assess what happened, report it to the FDPIC where required and inform the people affected.
From the blog
How we work on these topics, explained in full.
Cybersecurity for SMEs: protecting business data in 2026
Cybersecurity is now a priority for every Swiss SME. In 2026 cyber threats are on the rise, and the new nFADP, together with the GDPR, sets strict data protection rules. Antivirus software alone is not enough to protect a company: you need secure backups, password management, staff training and constant monitoring.
Read the article · 3 minData protection in Switzerland: what companies need to do to comply with the nFADP
The new Federal Act on Data Protection (nFADP) has been in force since 1 September 2023, and in 2025-26 the authorities' checks are getting stricter. Documenting processing activities, obtaining clear consent, reporting breaches and designing secure systems are essential steps.
Read the article · 3 minData protection in Switzerland: a practical guide to the nFADP
Challenges and opportunities for businesses and professionals, in a fact sheet full of food for thought.
Read the article · 3 minBackup and disaster recovery for Swiss SMEs: how to protect your business data
Backup and disaster recovery are essential for Swiss SMEs that want to protect their data and ensure business continuity. Incidents, human error and cyberattacks can bring a business to a halt if the right systems aren’t in place. In Switzerland, the nFADP requires concrete measures to keep data secure.
Read the article · 3 min
What an external DPO costs
The data protection officer role taken on externally, for a fixed monthly fee.
External DPO
fixed fee
CHF 400/month
A steady point of contact for records of processing, data subject requests and dealings with the authority.
The external DPO fee is this and doesn't change with each month's workload. Compliance checks, impact assessments and one-off work are quoted separately: ask for a tailored quote.
Book a consultationDo you know whether your company complies with the nFADP?
Tell us what data you process and where it's stored: we'll tell you what needs sorting out first.